Tagged: reply

@troed Fair question. I honestly haven't given it much thought yet. Just saw that argument and realised I haven't taken steps one way or the other.
I guess in the end I also don't trust all search engines to obey the indexing rules. But at least I can block unauthenticated users from public timelines I realised now.
I chose social.<name>.<tld>
But the important point for me is that the other two options have weaknesses. Anyone can register <name>.social before the organisation gets there, so you really want the domain name you already are on, for purposes of trust.
When it comes to Mastodon, you don't know that is the software you will necessarily always be using. So that one's out. 😁
But when it comes to which subdomain, not as important, Though I obviously like the one (social) you suggested 😉
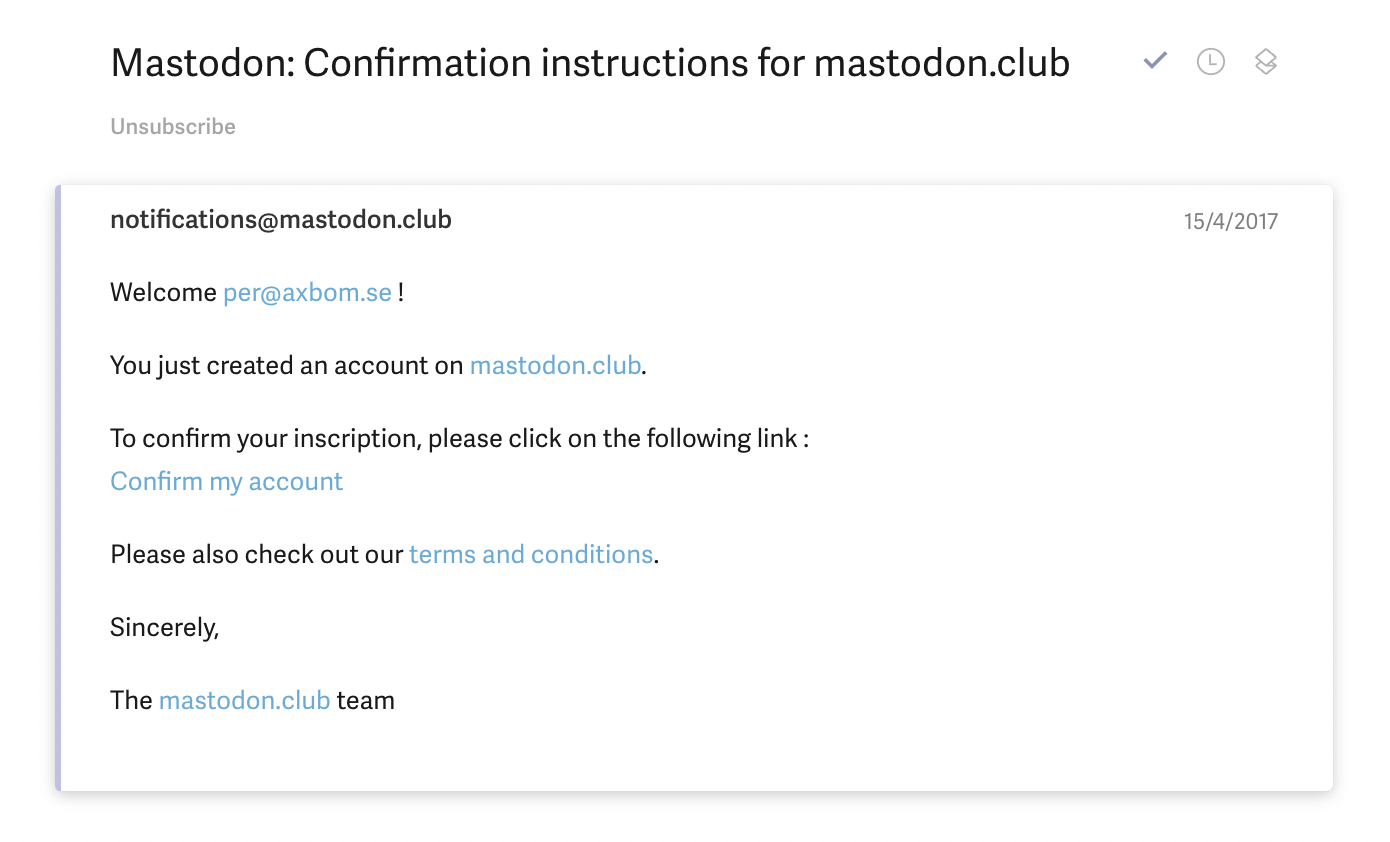
@evan This is what my confirmation email looked like in 2017. I gather this is the default email template from back then.
In my case I found the email but the instance doesn't exist anymore 😅
Almost. As I am a single-user instance (even though I have a few accounts) I can say that:
* boosts show in the home timeline when it is boosted, but in the federated timeline the boosted toots instead show at their own real timestamp, not as boosted
* if someone I follow sets their toot to followers only I only see it in Home.
* Replies between people I follow I only see in Home.
The federated timeline is the same for everyone on your instance.
Subtle differences.
@prosumer Ah I need to clarify this. I didn't realise the pro plan was needed for html widgets. Could be the case you can add a link href in the header instead. Can check this later today.
@prosumer As it turns out, the Pro plan ($19/year) is needed for both types of link verifications.
Sorry about that, will make it more clear in the post.
Hehe, I know the feeling. And today I really should have talked to you before I published my first musing at breakfast. 😅
On the other hand, it gave reason to talk to a lot of people, which was fun.
I'm excited about Mastodon but also keep seeing small problems all over the place.
Feel like it's important to address them and talk about them. You always do a fantastic job at this.
⚠️ GDPR + Mastodon
Love this multi-layered thinking. For every scenario there are always many more on top of that yet to be uncovered.
Just this example would help a lot of people understand the complexity of it all, and the importance of putting time and thought into doing the right thing and staying ahead of potentially damaging actions.
@Tattooed_mummy
Oooh. Thank you for taking the time replying to all those toots. 😊
⚠️ GDPR + Mastodon
Made a clarification here. What's written in the note can of course be very personal, but I am reminded personal notes are exempt from GDPR (unless the notes are made in a professional capacity, which means I still have questions around instances run by organisations)
I also have concerns about the vulnerability of storing data in this way, but that's a separate discussion. 😅
https://social.xbm.se/@axbom/109352443364669318
⚠️ GDPR + Mastodon
With regards to whether or not it applies to hobbyists, this is a great thread:
⚠️ re: GDPR + Mastodon
Made a clarification here. You're right that personal notes are exempt from GDPR (unless the notes are made in a professional capacity, which means I still have questions around instances run by organisations)
I also have concerns about the vulnerability of storing data in this way, but that's a separate discussion. 😅
⚠️ GDPR + Mastodon
Yes, you're right. I made a clarification here. In most cases it would appear these notes are indeed exempt from GDPR, unless the instance is run in a professional capacity and writing those notes is done as part of company/organisation operations.
Exactly. Which makes the conversation interesting and perhaps there are grey lines? A sports club, a media organisation... is it always clear when it's private or performed in a capacity as representing an organisation? Does it have to apply to a whole instance or to the specific use-case?
I guess it's similar to company email...
Good points. I feel like very little data nowadays is unstructured because the tools for sifting through it are so efficient at identifying it.
Another thought: let's say a public company sets up an instance and employees have accounts there. The employees write notes about customers who have Mastodon accounts, as part of their workplace tasks...
Is it still a private note?
@phf Oh no I enjoy the conversation. And you're likely right @abbe98 pointed out to me that there is an exemption for personal notes.
My worry is that personal data that can be very damning (political views, religion, etc) is stored digitally in notes in places where there is a responsible entity (the admin owner) but the security measures are largely unknown. How many have access?
So targeted attacks to retrieve profile info can potentially uncover a lot of personal data on large instances.
My thinking was not that I would need to know what information is stored about me. The reason i request information is to learn what information is stored in that entity's databases about me.
My first thought was that admin's would have to include any personal notes (not author's of those notes) as they could hold all that info in their database.
But as @abbe98 taught me, I would never learn (at least in that scenario and according to GDPR) that info about me is stored.
From my perspective, if I request from a server admin all the data that is stored about me on their platform, I would expect it to be revealed if someone is writing down my religion, home address, etceteras in a database they own.
Who wrote the note would likely not be revealed.
If I'm not allowed to know this, it's an interesting dilemma...
⚠️ GDPR + Mastodon
Yes, upon a request it would not be revealed who wrote it.
But if I do request, I would consider it of interest to know if someone has written down my home address, religion, children's names and more...