
↪ Replying to @EmilOberg
@EmilOberg This is likely what my honest response would be as well. Thanks.
↪ Replying to @FCCoachJohan
@FCCoachJohan Haha, love the honesty of this. Thanks!
On a scale of 1-10, how certain are you that none of your social media or email accounts have been compromised, meaning that someone logs into it from time to just read stuff or like things from your account?
1 = I’m likely compromised.
10 = I’m 100% certain I am safe.
With just a few responses to this it is immediately obvious that very tech-savvy individuals using two-factor authentication will still avoid committing to a 10. I believe this is an important insight for all internet users.
↪ Replying to @beantin
@beantin @marcusosterberg Now reminded of my dad saying “First and främst” when he gave speeches in English. 😅
↪ Replying to @beantin
@beantin Also, none of those g's sound like you're collecting saliva to spit. Which might be sounding 'engaGemang' a bit too hard 😂
↪ Replying to @beantin
@beantin Good point. I hadn't even thought about all those different g sounds 😅 The second one being the most non-intuitive of all.
↪ Replying to @unknown
@yoghurteater You may want to follow @web3isgreat for your regular reminders on why you don't really need to know... 😅
x.com/web3isgreat/st…
Att man inte ska klicka på länkar från okända avsändare är många medvetna om. Men, hur tänker du och ditt företag med säkerheten kring QR-koder?
"Att scanna en okänd QR-kod är läskigt nära beteendet att sätta in en okänd USB-sticka i sin dator", skrev integritetsexperten Calli Schroeder nyligen på Twitter.
QR-koder innebär nu att det kan bli ännu lättare att lura in människor på illvilliga webbsidor, trigga skript och fiska efter lösenord eller andra personuppgifter.
Problembilden förstärks av att man inte ser skillnad på en "snäll" och en "elak" QR-kod. Och precis som i många andra phishing-attacker behöver du inte ens märka att du blivit utsatt, eftersom du efter hand kan ledas vidare till den sida du förväntade dig.
Jag kan till exempel trycka upp klistermärken med mina egna QR-koder som jag klistrar ovanpå QR-koder på restauranger, bankkontor, event, kontor, butiker, och så vidare. En kod det ser ut som att du förväntas scanna kan alltså vara lömsk. Hur skulle du se skillnad?
"På webbadressen innan man klickar" svarar kanske en del. Men, handen på hjärtat, hur många tror vi aktivt hejdar sig och granskar en kanske felstavad webbadress?
Jag skulle också kunna dela ut "oskyldig" direktreklam i brevlådor med massor av fina QR-koder som till exempel innebär att du "vinner priser".
Det kan alltså vara läge att påminna kollegor, familj och vänner om riskerna med QR-koder. Hur roliga de än må vara att scanna.
p.s. Scanna koden i min bild. Den är säker. Jag lovar. 🤞
↪ Replying to @_trantom
@_trantom Awesome, thank you! 🙌 Main difference is that mine would likely be in Swedish. 😁
x.com/axbom/status/1…
Now I have this wonderful research idea thanks to @Iwillleavenow's QR code tweet yesterday. Putting up QR code stickers in strategic places at Stockholm central station to measure how many people will scan them during a month.
Have this idea of starting a podcast called "A completely normal f**ing person". And just do 30-minute interviews with people from all walks of life that I meet on the street. I feel there are just so many experiences we rarely hear about.
Won't happen anytime soon though… 😬
The alternative would be finding two people to interview each other, which could be all kinds of insightful. Different interviewer and interviewee each time. I just help with recording and distribution.
All of this has probably been done already of course.
Case in point. This will be fun to listen to. x.com/_trantom/statu…
Another tip, via @steveportigal
"With a focus on New York City, [this newsletter] takes a fresh look at the everyday, delights in the absurd, and often features profiles of unusual folks who truly do things their way."
annekadet.substack.com/about
You may know there’s a common practice on LinkedIn of posting links in comments rather than the post itself. Supposedly this ”tricks the algorithm”.
I see this is as non-inclusive behavior, adding hefty effort for many people with impairments. Happy to hear thoughts / examples.
There’s also this: x.com/forssto/status…
Jag lanserar ett nytt sätt att anlita mig. Ett sätt som ger bästa tänkbara användning av hela bredden av min expertis. Principen är enkel:
Anlita mig 1, 2 eller 3 dagar i månaden på årsbasis. Varför det är smart kan du läsa mer om på min sida ”Digital drivkraft”.
Another thing to remember is how easy it is to print QR code stickers and just stick those over legitimate stickers at restaurants, events, stores, offices, banks, etceteras. They look the same to you.
So even a code it seems you are expected to scan could be a malicious one. x.com/Iwillleavenow/…
↪ Replying to @dsign4life
@id8_4good 😊. I do like the Internet. I'm just not a fan of how it is distributed.
↪ Replying to @ApVeng
@ApVeng Many seem to fit the bill, but neither of these were in the quote.
”X has made a calculated business decision to allow users to egg each other on to violence against named politicians with zero consequences, just as they allow anti-vaxxers, incels and other fringe extremists to congregate on their platform.”
Solve for X.
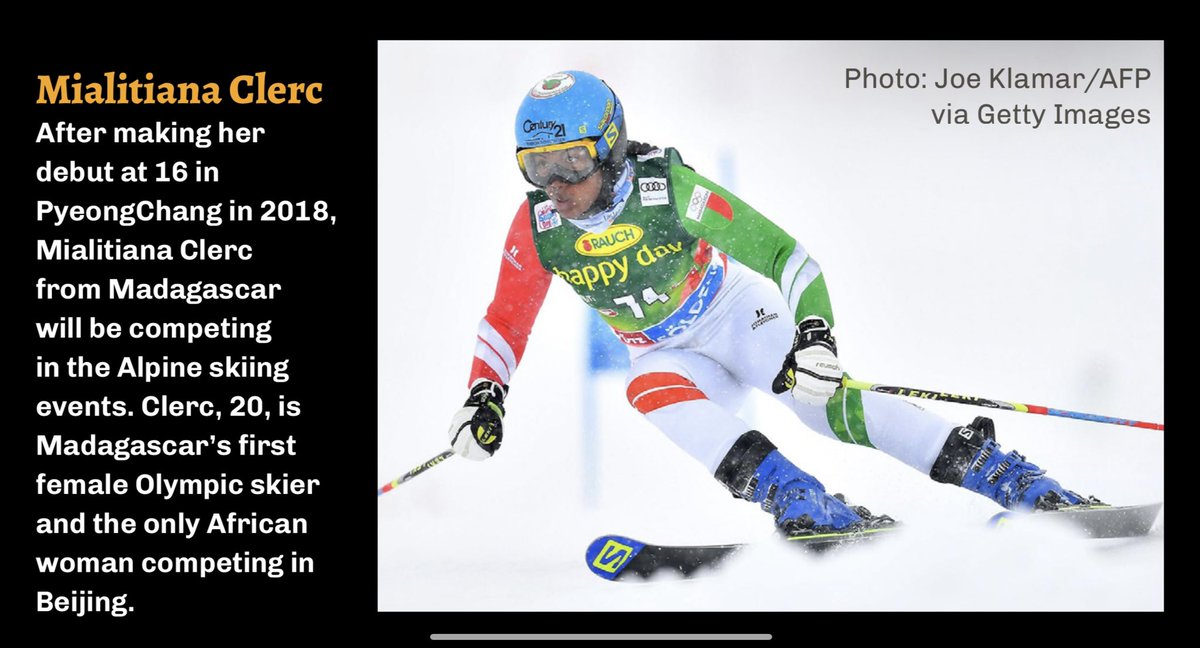
8 African nations were represented by 13 athletes at the 2018 Olympics, but this year's games have only 5 African nations and 6 athletes, all in Alpine skiing and cross-country. A continental quota system established in 2016 was dropped in 2019, without any real explanation.
”Skeleton athlete Akwasi Frimpong: ”I have a vision of seeing more African athletes in winter sports. It’s something I carry in my heart. For me, it’s very important to be able to turn on the TV and see my brothers and sisters that look like me compete in winter sports,
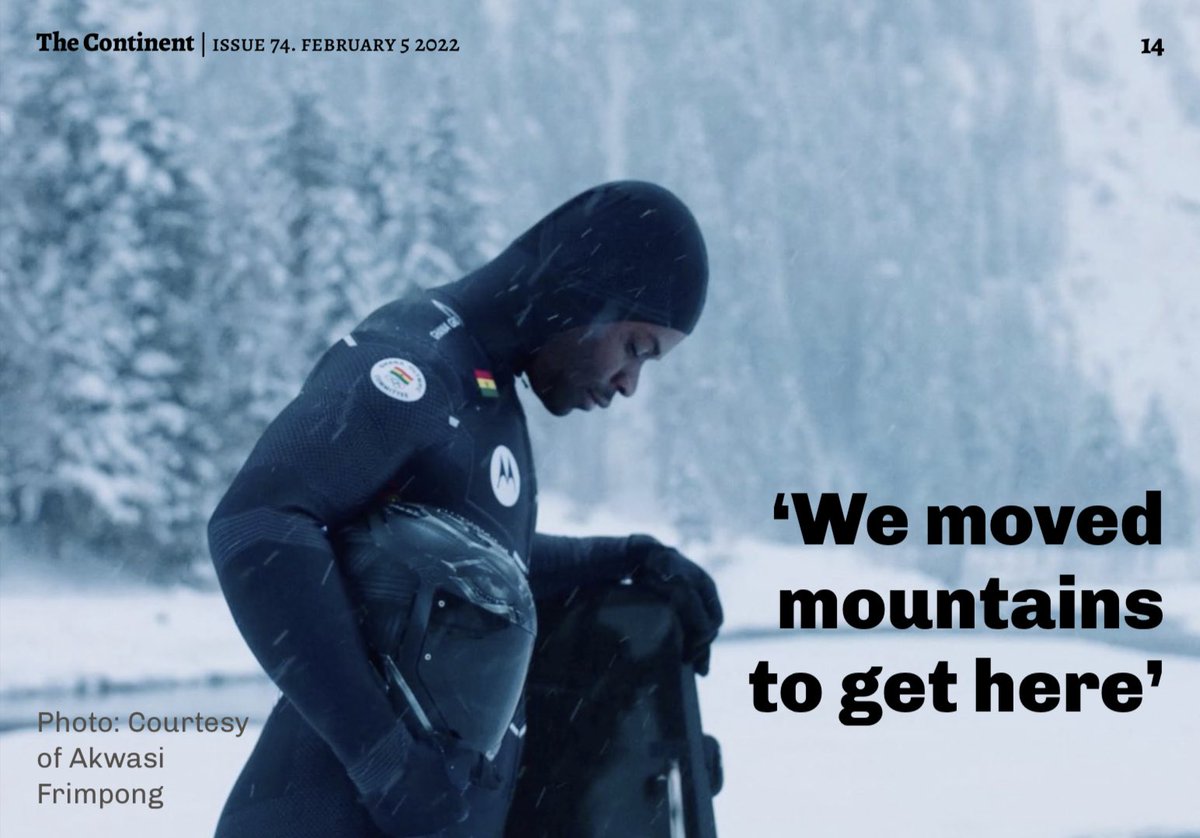
and I was really hoping to see more African athletes at the 2022 Olympics. But we are half of what we had in 2018. We’re overlooked. We don’t have a seat at the table. Who is sitting at the table to represent Africa? Nobody.”
-Issue 74 of @thecontinent_
youtube.com/watch?v=PB7NnI…